One token for several Regions
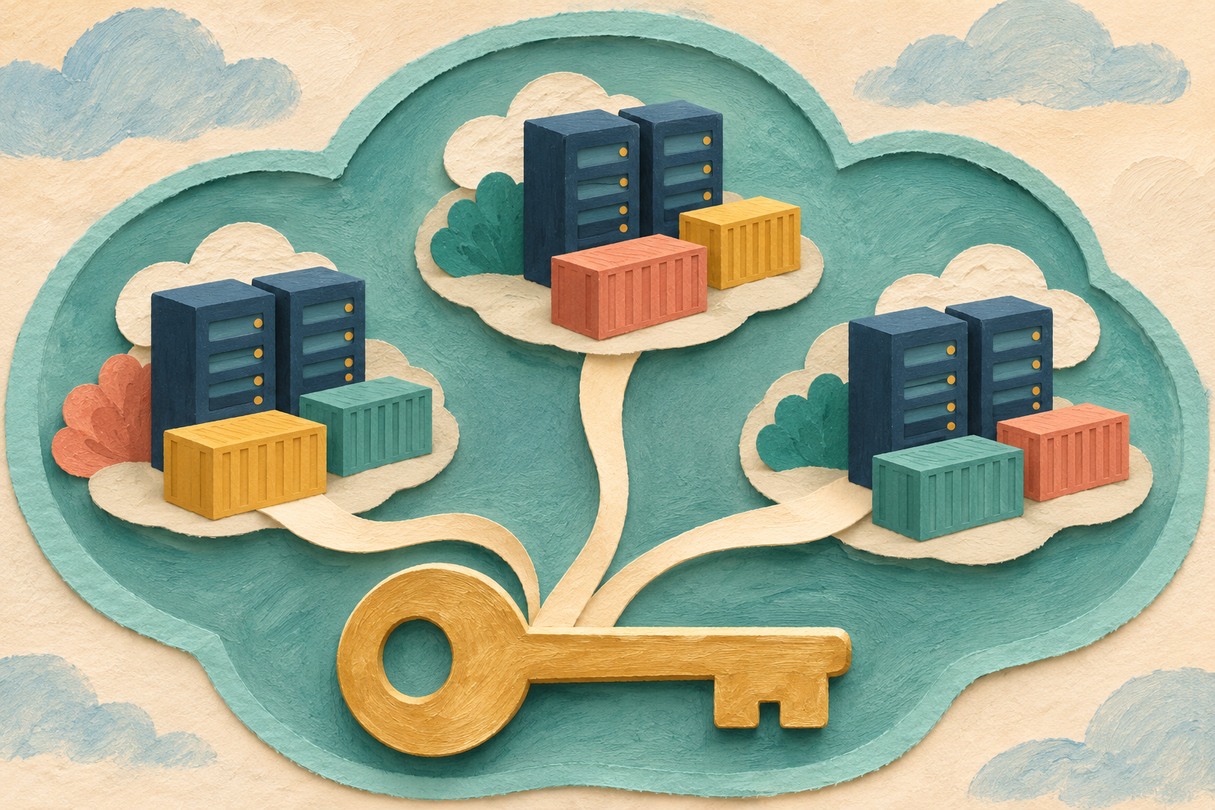
Amazon ECR announced global authentication tokens for private registries on November 17. A token obtained through the AWS Sign-In CreateBearerToken API can be used across ECR private registries in the same AWS partition.
Previously, image pushes and pulls needed a separate token for each Region. AWS highlights multi-Region container-pull proxies as a use case where the change reduces token coordination.
Validity and existing workflows
The default token lifetime is 12 hours, configurable down to five minutes. AWS says the tokens work with the Docker CLI and Amazon ECR Docker Credential Helper.
Existing regional tokens continue to work. The announcement does not say teams must immediately replace them.
Availability and next steps
AWS lists availability in all commercial Regions that support ECR. The shared-token scope is within one partition; cross-partition access is not promised.
The announcement links its private-registry authentication guide for teams reviewing their workflows. No token was created and no production credentials were changed for this report.